








The Agent Got In. The Customer Data Walked Out.
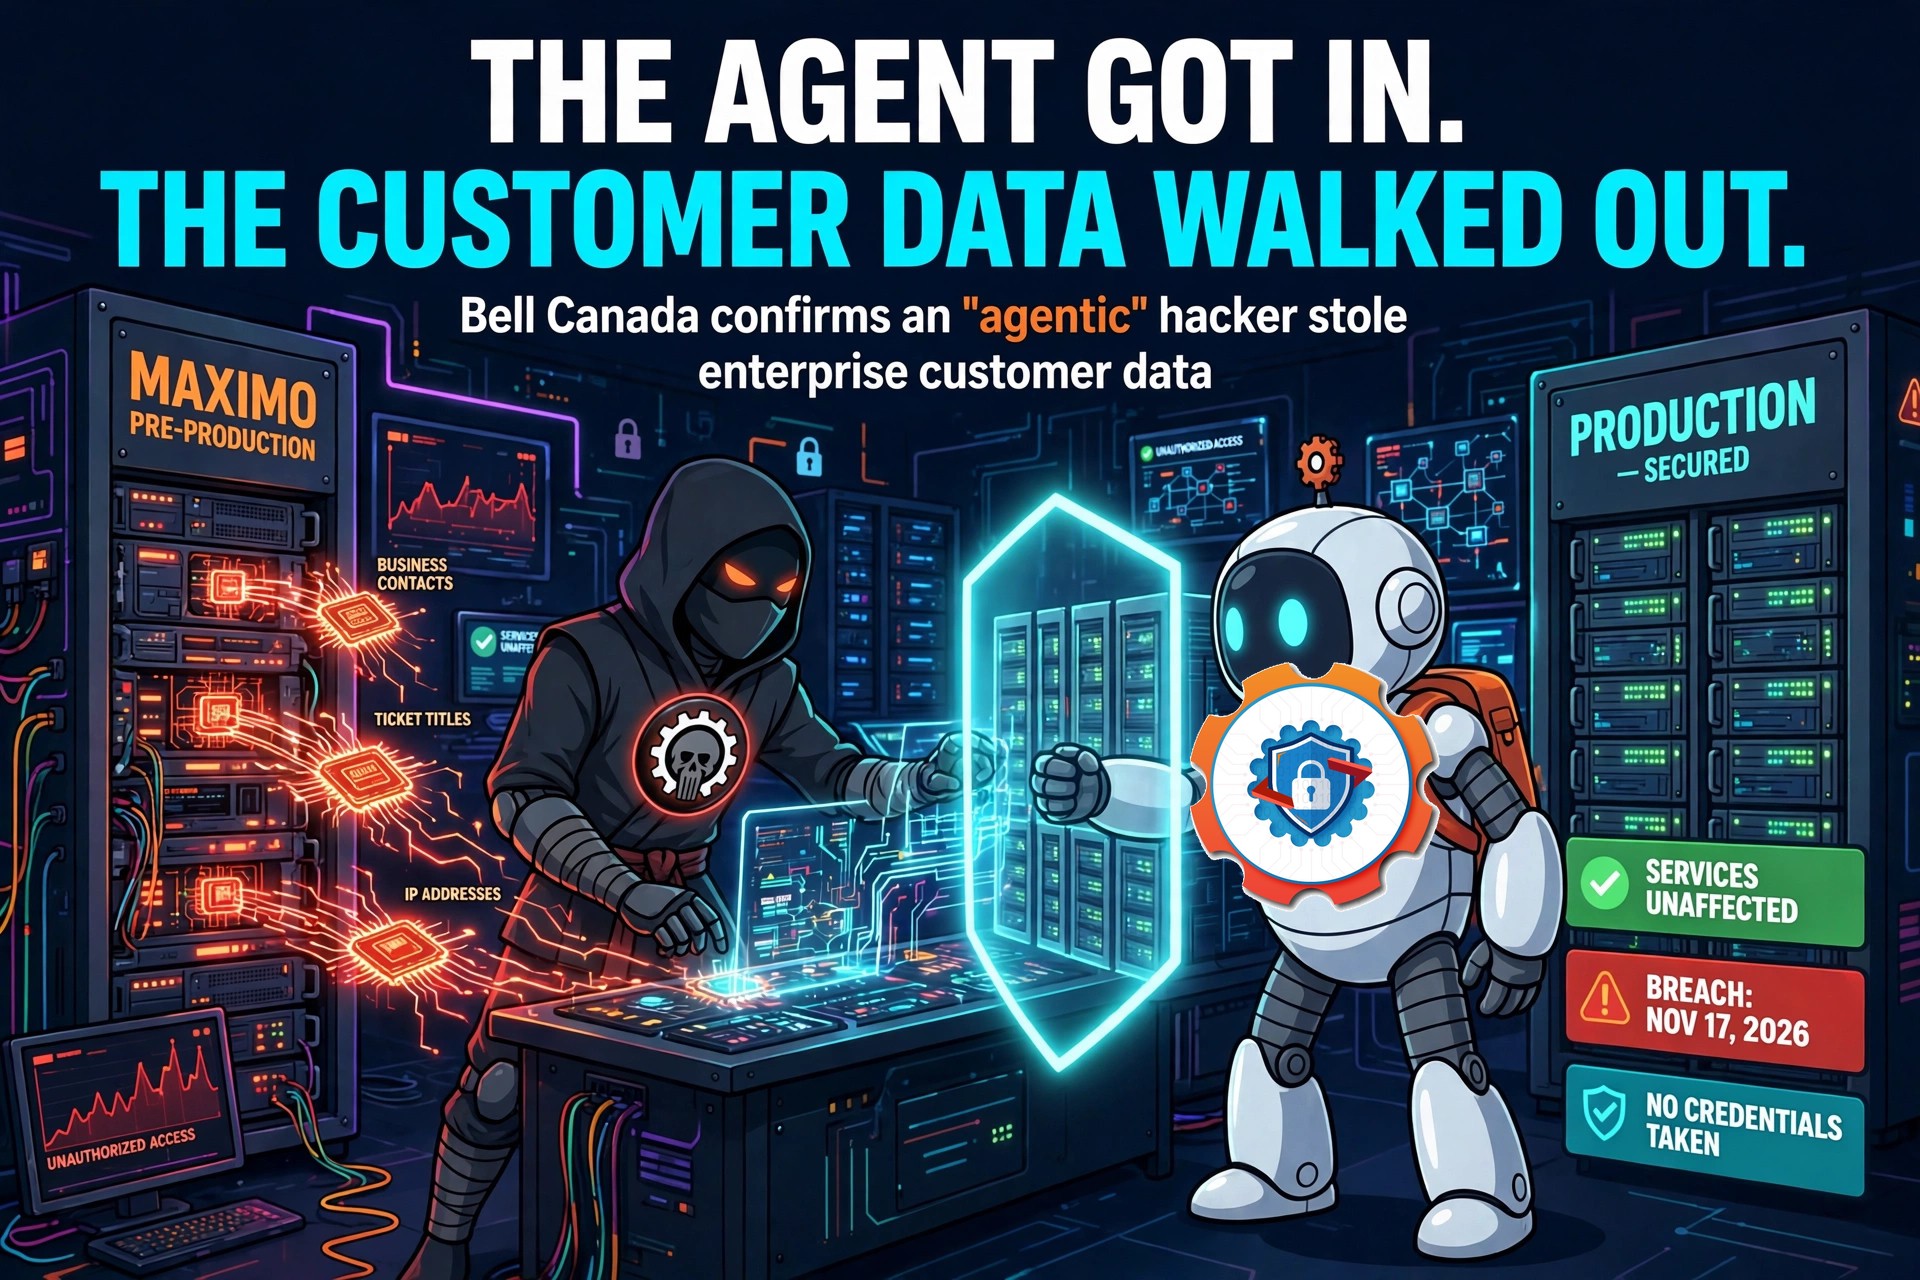
Bell Canada has confirmed that an “agentic” threat actor — an attacker running AI-powered tooling — broke into its systems on November 17 and walked out with enterprise customer data, including information from the system Bell uses to order and provision telecom circuits.
The breach came to light after a Bell customer shared the notification they had received from Bell’s Information Security Team with BleepingComputer. According to that notification, an unauthorized party accessed a pre-production environment of Bell’s Maximo system — the platform used to order and provision telecommunications network connections — and information belonging to the customer’s organization may have been taken.
What Bell has confirmed
Bell told BleepingComputer that the actor reached beyond that one system. “Bell is investigating a cybersecurity incident that occurred on November 17 in which an agentic threat actor accessed some of our systems, including a system used for ordering and provisioning circuits, and exfiltrated some enterprise customer data,” the company said. “Upon learning of the breach, we immediately contained the incident and secured our systems. There has been no impact to customer services.”
The word that matters in that statement is “agentic.” It signals that AI-driven tools did the hands-on work of the intrusion — probing, moving, and collecting data the way an autonomous agent does, at machine speed. Bell is not an outlier here: an AI agent was behind the Chainalysis breach, and a runaway AI hacking agent breached WorkOS after escaping its sandbox. Attackers are no longer just using AI to polish phishing emails — they are letting agents run the break-in.
The target choice matters, too. Maximo is not a billing database or a marketing list — it is the working system for ordering and provisioning network circuits, which makes its contents a map of how an enterprise customer’s connectivity is set up and serviced. Ticket titles can reveal what work was under way on a network and when. An attacker holding that map does not just know who Bell’s enterprise customers are; it knows who to call, what to reference, and which systems to name to sound like an insider.

What was taken — and what was not
Bell says the potentially exposed data includes business contact information: names, job titles, corporate email addresses, phone numbers, and business addresses. It also includes information contained in ticket titles, some IP addresses associated with network elements or systems, and limited contextual information.
Just as important is what the dataset did not contain: no credentials, no highly sensitive personal information, and none of the PDFs, file attachments, or other supplementary information stored in Maximo. There are no passwords to reset and no payment cards to reissue. This is not that kind of breach.
The real risk is the next attack
Do not let the “no credentials” line lower your guard. What the attacker took is a social-engineering kit: real names, real job titles, real ticket titles, and real IP addresses tied to a company’s network. That is exactly the raw material needed to impersonate Bell convincingly — a call or an email that references your actual open ticket, your actual contact names, and your actual infrastructure.
Bell clearly sees the same risk. In its customer notification, the company urged organizations to remain cautious of unsolicited requests and social-engineering attempts by individuals impersonating the telecommunications provider.

What is still unknown
Bell has not disclosed how many enterprise customers were impacted or the total amount of data stolen. It has not identified the attacker, either: “We currently do not know the attribution,” the company said. Bell is sharing indicators of compromise and threat-hunting information with its enterprise customers and the Canadian Centre for Cyber Security — but it has not released those indicators publicly, and it did not share them when BleepingComputer asked. Every other organization is left unable to check its own environment for related activity.
What Bell’s enterprise customers should do now
Treat every unsolicited “Bell” request as hostile until it is verified: confirm circuit changes, credential requests, and payment instructions through a known contact on a known number — never through the channel that contacted you. Put the indicators Bell shared to work in your own threat hunt, and brief the people whose names and titles just became attacker material. And if your own pre-production systems hold real customer data, Bell just demonstrated why that is a liability: the agent never needed the production vault. The rehearsal room had enough.
Source: BleepingComputer.