






A Decade in the Code. No Login Required.
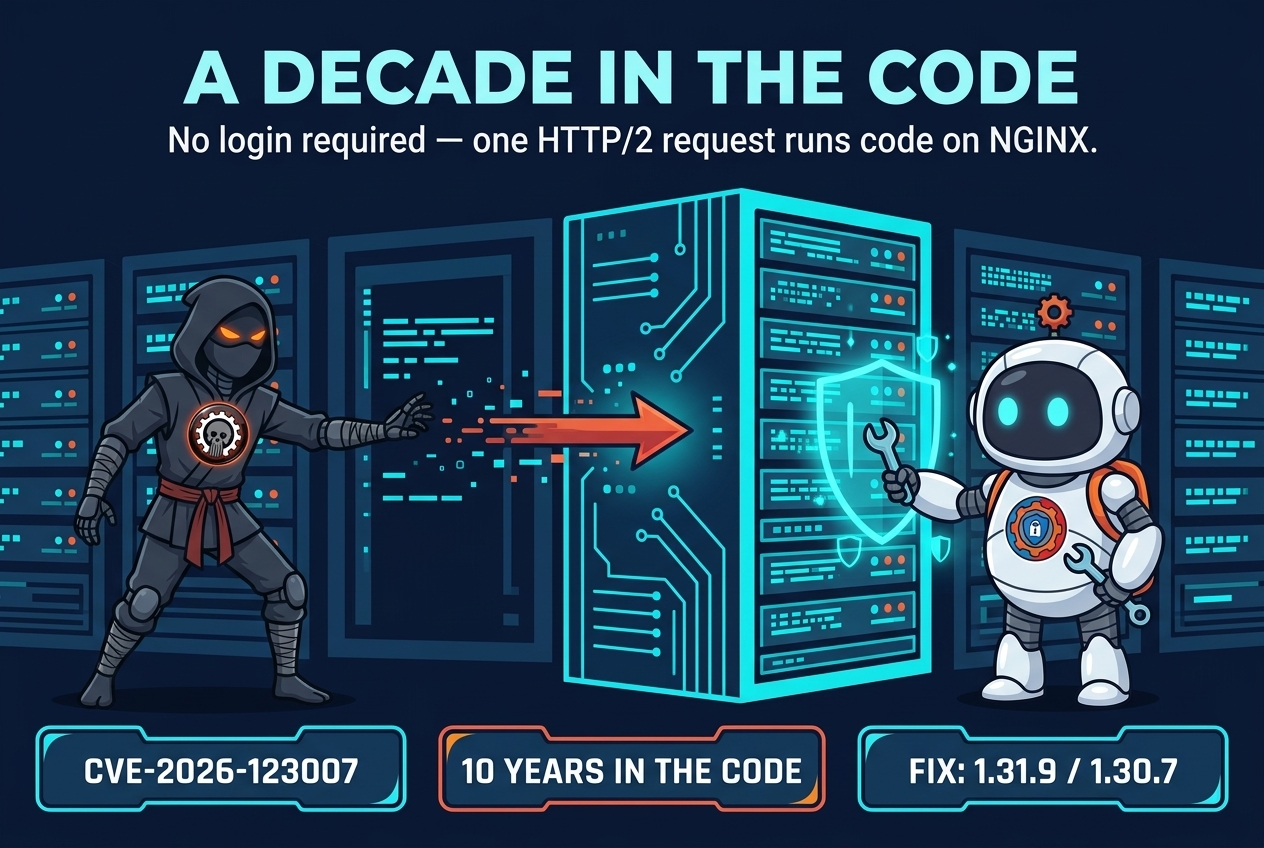
Ten years. That is how long a flaw sat in the HTTP/2 code of NGINX, one of the most widely used web servers on the internet, waiting for someone to send the right request. On November 18, F5 — the company behind NGINX — shipped the fix. The flaw, tracked as CVE-2026-123007 and dubbed “nginx2root,” lets an attacker run their own code on a server with HTTP/2 turned on. No login. No password. Just a reachable port.
The bug has been in NGINX’s open-source code since version 1.9.5, released in September 2015. Every open-source release from 1.9.5 through 1.31.8 is vulnerable. NGINX Plus is affected too, in 37.x releases before the fixed builds and in R34 to R36. Fixed versions 1.31.9 and 1.30.7 are out now, with official Docker images already tagged.
How the attack works
Modern servers randomize where code and data sit in memory — a defense called ASLR. F5 says this flaw lets attackers run code where ASLR is turned off, or where it can be bypassed. Researchers did both: Wiz bypassed ASLR and ran code in tests, and Xint ran code with nothing more than a reachable HTTP/2 port.
Code executed this way runs with the permissions of an NGINX worker process. Getting root takes a second privilege-escalation bug — and Xint found one, in the Linux kernel’s SCTP code, reaching root even when NGINX ran inside a Docker container.
The attack is not a quick knock: Rapid7’s version needs about 128 GB of HTTP/2 traffic over two and a half minutes, on a connection faster than about 300 Mbit/s, and it depends on a glibc memory-copy routine chosen on x86-64 CPUs with the AVX-512 features avx512f and avx512vl. A real constraint — but not much of one on a fast server with the right chip.

Five flaws, one release
The November 18 releases also fix four more flaws that F5 says can lead to code execution under the same ASLR condition. All five score 9.2 on CVSS 4.0, and each needs a particular setup:
- CVE-2026-123007 — HTTP/2 turned on. The nginx2root flaw.
- CVE-2026-123633 — HTTP/2 on, requests passed to a backend while the worker runs low on connections.
- CVE-2026-123634 — a proxied server name built from variables, plus a server-side include or mirror subrequest.
- CVE-2026-121810 — HTTP/3 turned on.
- CVE-2026-113425 — NGINX used as a mail proxy.
Versions 1.31.9 and 1.30.7 fix all five; on NGINX Plus, builds 37.3.0.1 and 37.0.8.1 fix four. For Plus R34 to R36, no fix is listed yet.
Why it matters now
Three things make this urgent. First, proof-of-concept code is already public on GitHub. Its notes say it is only a demonstration against a fresh Docker container on the same machine — but public proof-of-concept code has a habit of getting better fast. Second, neither F5 nor the researchers have reported any attacks exploiting the flaw so far, and CISA’s Known Exploited Vulnerabilities catalog does not list it. Good news, but also a window: the fix is out, the method is public, and every unpatched server is now on a clock. Third, the patches have not reached everyone yet: Ubuntu and Debian had not shipped fixed packages when the story broke, and a distribution package can carry a fix without changing the version number nginx -v reports — compare the full package version against the distribution’s own advisory.
It is not the first decade-old flaw in network code this month — a Linux kernel TCP bug we covered recently hid for eleven years.
What to do
1. Check whether you are exposed. HTTP/2 is on where a listen directive includes http2, or where http2 on is set. Test with openssl s_client -alpn h2: if the output reads ALPN protocol: h2, the server accepts HTTP/2. Behind a CDN, test the NGINX origin itself.
2. Upgrade — and restart properly. Move to 1.31.9 or 1.30.7 (or the fixed Plus builds), then restart NGINX fully or use its live binary upgrade. A reload alone leaves the old executable running, and existing connections can stay on old worker processes.
3. If you cannot patch yet, turn HTTP/2 off. CIRCL, Luxembourg’s incident response center, lists disabling HTTP/2 as a temporary mitigation: it blocks CVE-2026-123007 and CVE-2026-123633, though not the other three flaws, and turning off HTTP/3 where it is used removes the setup CVE-2026-121810 needs. On NGINX 1.25.1 and later, set http2 off; in each affected server block and remove http2 from its listen directives; on older versions, just remove http2 from the listen directive. Restart, then rerun the openssl check to confirm the server no longer accepts HTTP/2.
4. Block the SCTP escape hatch. Until the Linux kernel’s SCTP bug is fixed, the same guidance advises hosts that do not use SCTP to block its kernel module from loading with install sctp /bin/false in a file under /etc/modprobe.d/. That does not unload a module already loaded, or turn off SCTP built into the kernel. The same prize — root with no login — came through a different hole in a Linux TCP flaw we covered earlier this month.
5. Watch for signs of an attack. CIRCL suggests looking for workers starting unexpected programs, abnormal exits or core dumps, long-lived HTTP/2 connections with heavy traffic but few logged requests, and unusual outbound connections or DNS lookups. A clean access log does not rule out an attack — HTTP/2 control frames do not normally show up there as requests. None of these signs proves an attack alone.

A ten-year-old flaw in one of the internet’s most common web servers, a public proof of concept, and a fix that is already out. The gap between those last two facts is the whole story — close it before someone else does.
One thought on “A Decade in the Code. No Login Required.”