



The Ransom Failed. The Data Went Public.
The leak site post went up. The data followed.
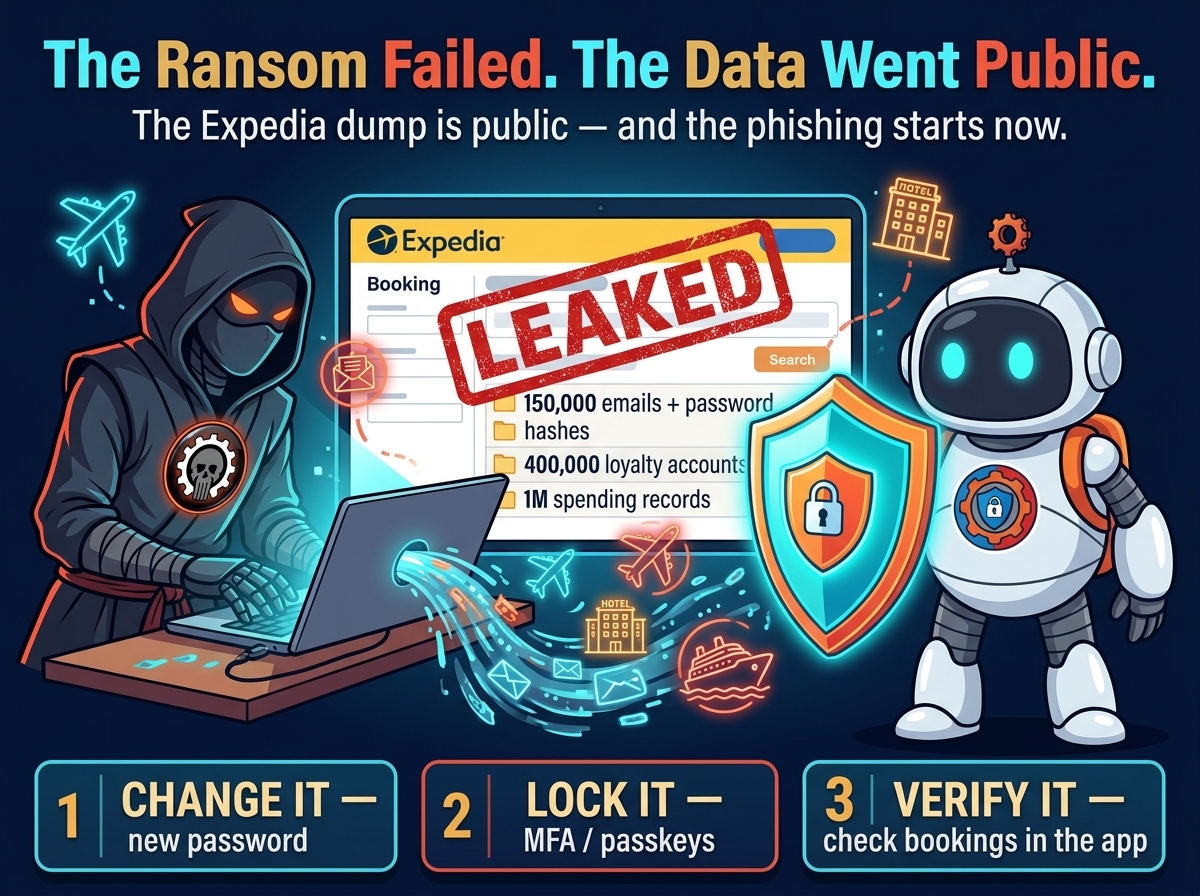
In early October, a ransomware gang calling itself n0n added Expedia to its dark-web leak site, claiming to hold roughly one billion records stolen from the travel giant. Now the silence has broken in the worst way: the gang has published a dataset of more than 500 megabytes that it says came from Expedia’s systems. When stolen data goes public like this, it usually means one thing — the ransom talks failed, and the attackers decided to punish the refusal by giving the data away.
Researchers at Cybernews examined the files and verified what is inside. The dump is not one customer list. It is several datasets from different parts of Expedia’s operation, spanning more than a decade:
- About 150,000 consumer account records — email addresses plus bcrypt password hashes, dated 2011–2018.
- About 100,000 booking order events from 2018 — booking confirmations and customer emails.
- About 400,000 loyalty program accounts running up to 2025 — emails, program details, plan names.
- About 200,000 cruise passenger emails, in a file dated October 2024.
- About 500,000 fraud evaluation records — emails paired with fraud-check statuses.
- About 120,000 traveler profiles — emails and timestamps.
- About 350,000 reference records that link the other datasets into fuller profiles.
- About one million spending-pattern records — estimated customer spending on accommodation, car rentals, and travel services.

Why this matters more than an old email list
Some of this data is old, and it is tempting to shrug at account records from 2011 to 2018. That would be a mistake. First, the newest material runs to 2025 — loyalty records and spending patterns current enough to be useful right now. Second, the datasets link together. A lone email address is a nuisance; an email tied to real booking confirmations, a loyalty plan, cruise history, and spending habits is a convincing identity — exactly the raw material for phishing that does not look like phishing.
Third, the passwords matter even though they are hashed. The account records include bcrypt password hashes — strong, but “strong” is not “unbreakable.” Weak and common passwords fall to offline cracking, and these hashes are now in the hands of anyone who downloads the dump. The real danger is the account you forgot about: an Expedia login created in 2014, never used since, with a password you reused on three other sites. That password is now crackable at an attacker’s leisure, and the account it protects may still be live.
What is confirmed — and what is not
Honesty matters here, because the claim and the proof are not the same thing. Expedia has not confirmed that this data is theirs, or that a breach of this scale happened; Cybernews says it is awaiting a response. What the researchers have verified is that the files are real data, in the volumes and formats described above, and consistent with Expedia customer records. That is strong evidence — but it is not Expedia’s confirmation, and this article will not present it as one.
What Expedia has confirmed is the break-in itself. On November 12, Expedia Group said attackers had reached its systems through a compromised third-party data platform provider — the incident we covered in They Got In Through the Vendor. Expedia Just Confirmed It. The entry point appears to have been the Qubole breach, in which attackers abused trusted AWS access to reach customer cloud environments — a supply-chain failure we examined in One Vendor Key, Every Customer’s Cloud. Neither Expedia nor the researchers who disclosed that breach have publicly confirmed the link, but the timing and method line up. Expedia has still not named the vendor or said what data was taken. This dump may be the answer to that second question — allegedly. Until Expedia speaks, it remains the gang’s claim, backed by researcher-verified files.
Expedia Group also runs Hotels.com, Vrbo, Travelocity, Orbitz, Hotwire, and Trivago.
What travelers should do now
If you have ever had an Expedia account, treat this as real and act today.

1. Change your Expedia password, and everywhere you reused it. Log in and set a new, unique password, then change the same password anywhere else you used it. Reuse is what turns one old leak into five compromised accounts.
2. Turn on multi-factor authentication — or better, passkeys. If Expedia offers MFA or passkey sign-in, enable it now. A stolen password is useless to an attacker who cannot pass the second factor, and a passkey cannot be phished at all.
3. Expect booking-detail phishing, and verify through the app. Treat any travel-related email, text, or call with suspicion — especially one that mentions a real trip, hotel, or cruise. Do not click links in the message. Open the Expedia app or type the site address yourself and check the booking there. Real details in a scam message are no longer proof the message is real.
4. Check whether your email appears in known breaches. A quick check on a service like Have I Been Pwned shows whether your address has shown up in breach data before.
The gap between “we were breached” and “here is what was stolen” is where the damage happens — and travelers are left to close it themselves. Change the password. Turn on the second factor. And the next time an email knows a little too much about your last vacation, do not click — verify.