
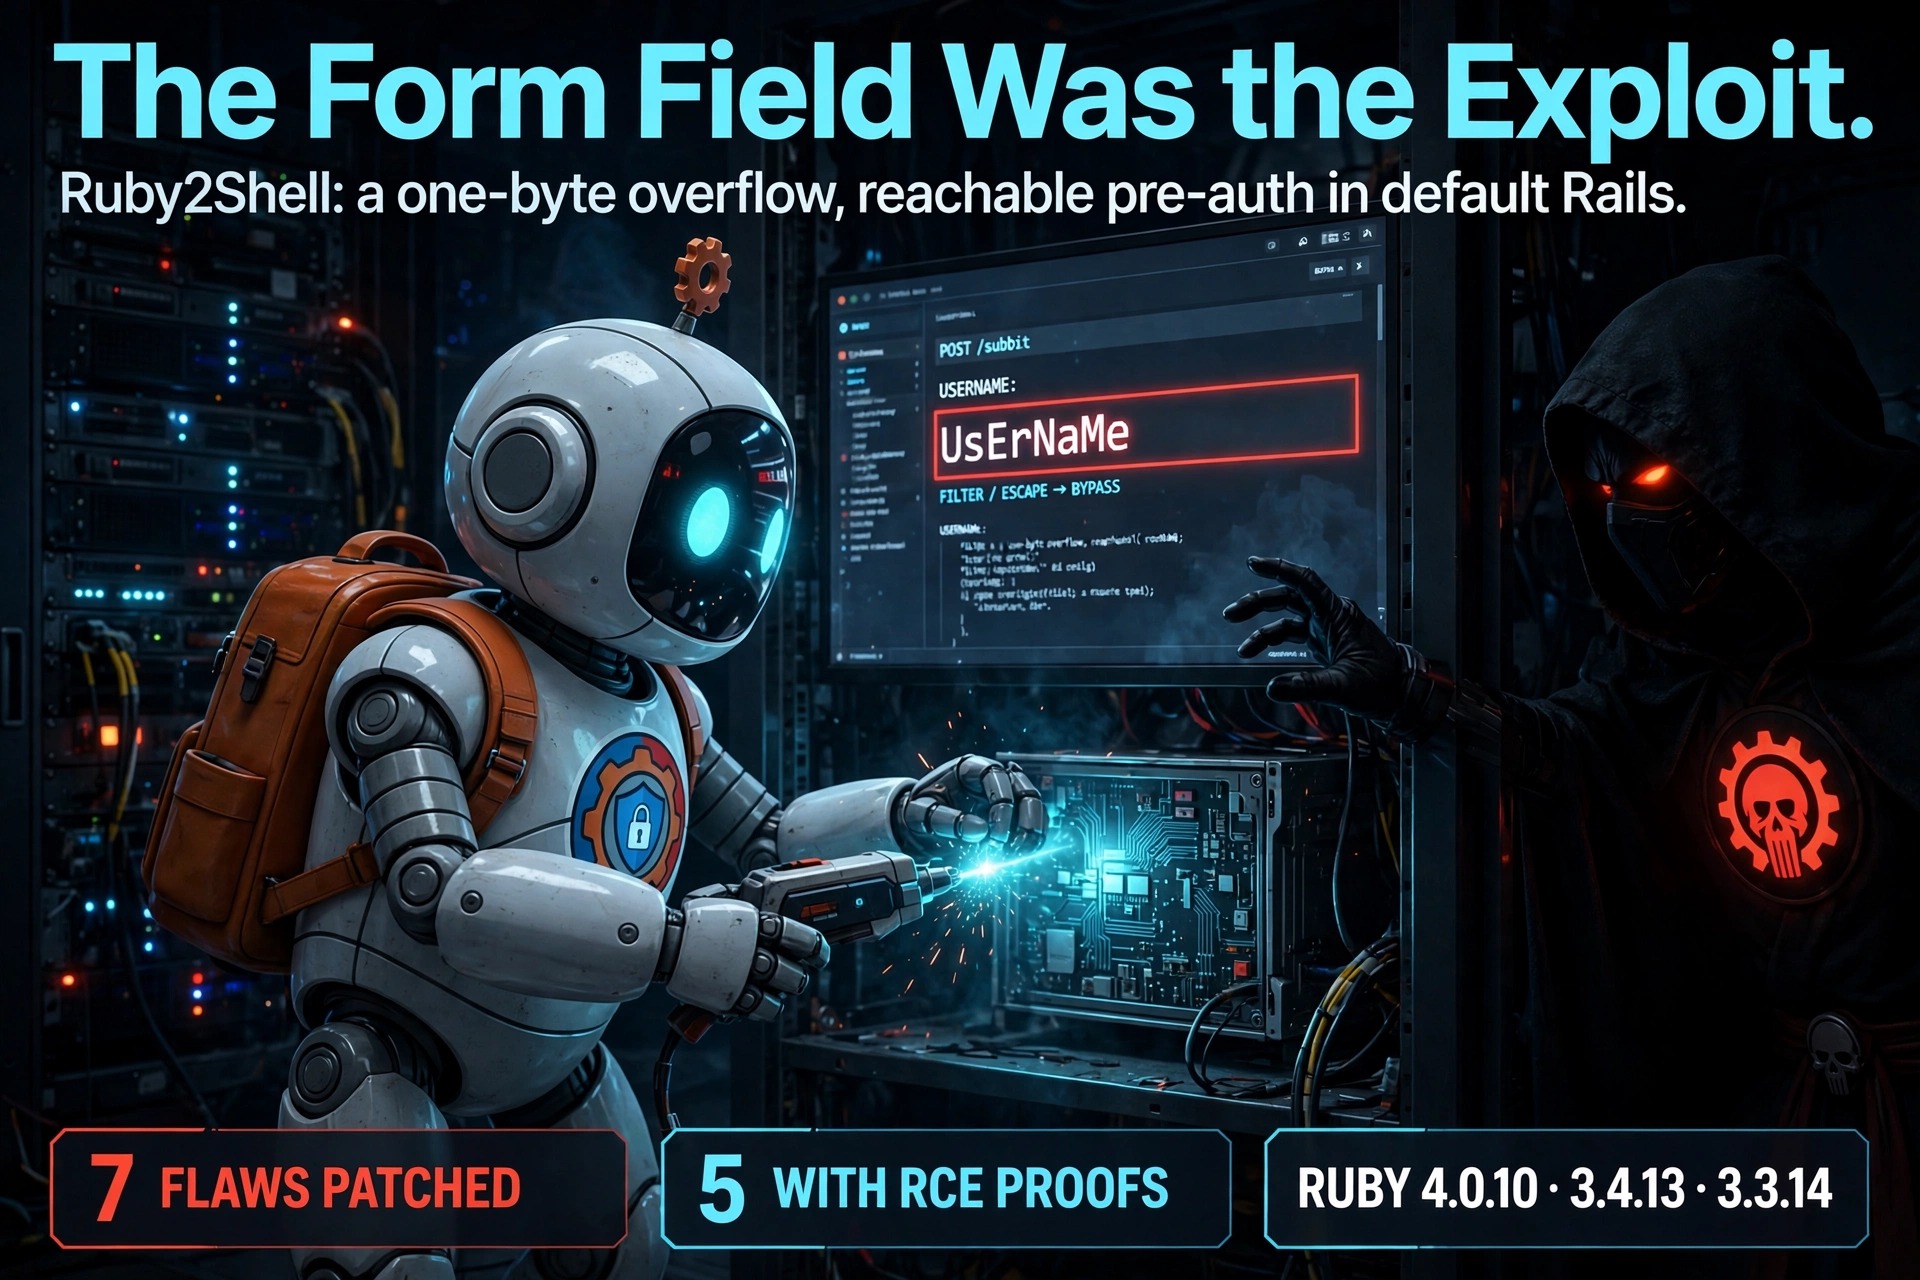
The Form Field Was the Exploit.
Nobody typed a payload. Nobody logged in. A visitor filled in a form field, hit submit, and the web framework itself did the dangerous work before a single line of … Read More

Cybersecurity, Technology & Engineering






Nobody typed a payload. Nobody logged in. A visitor filled in a form field, hit submit, and the web framework itself did the dangerous work before a single line of … Read More
Seven critical flaws. Every one of them scores 9.2. The PHP Foundation shipped emergency security updates on November 19 for all supported PHP versions, and the headline flaw — codenamed … Read More
The fix had been out for nearly a month. The attackers came anyway. On November 19, Russian cybersecurity firm F6 reported what appears to be the first in-the-wild exploitation of … Read More

