



40 Billion Fake Ads a Day. Built Into the Box.
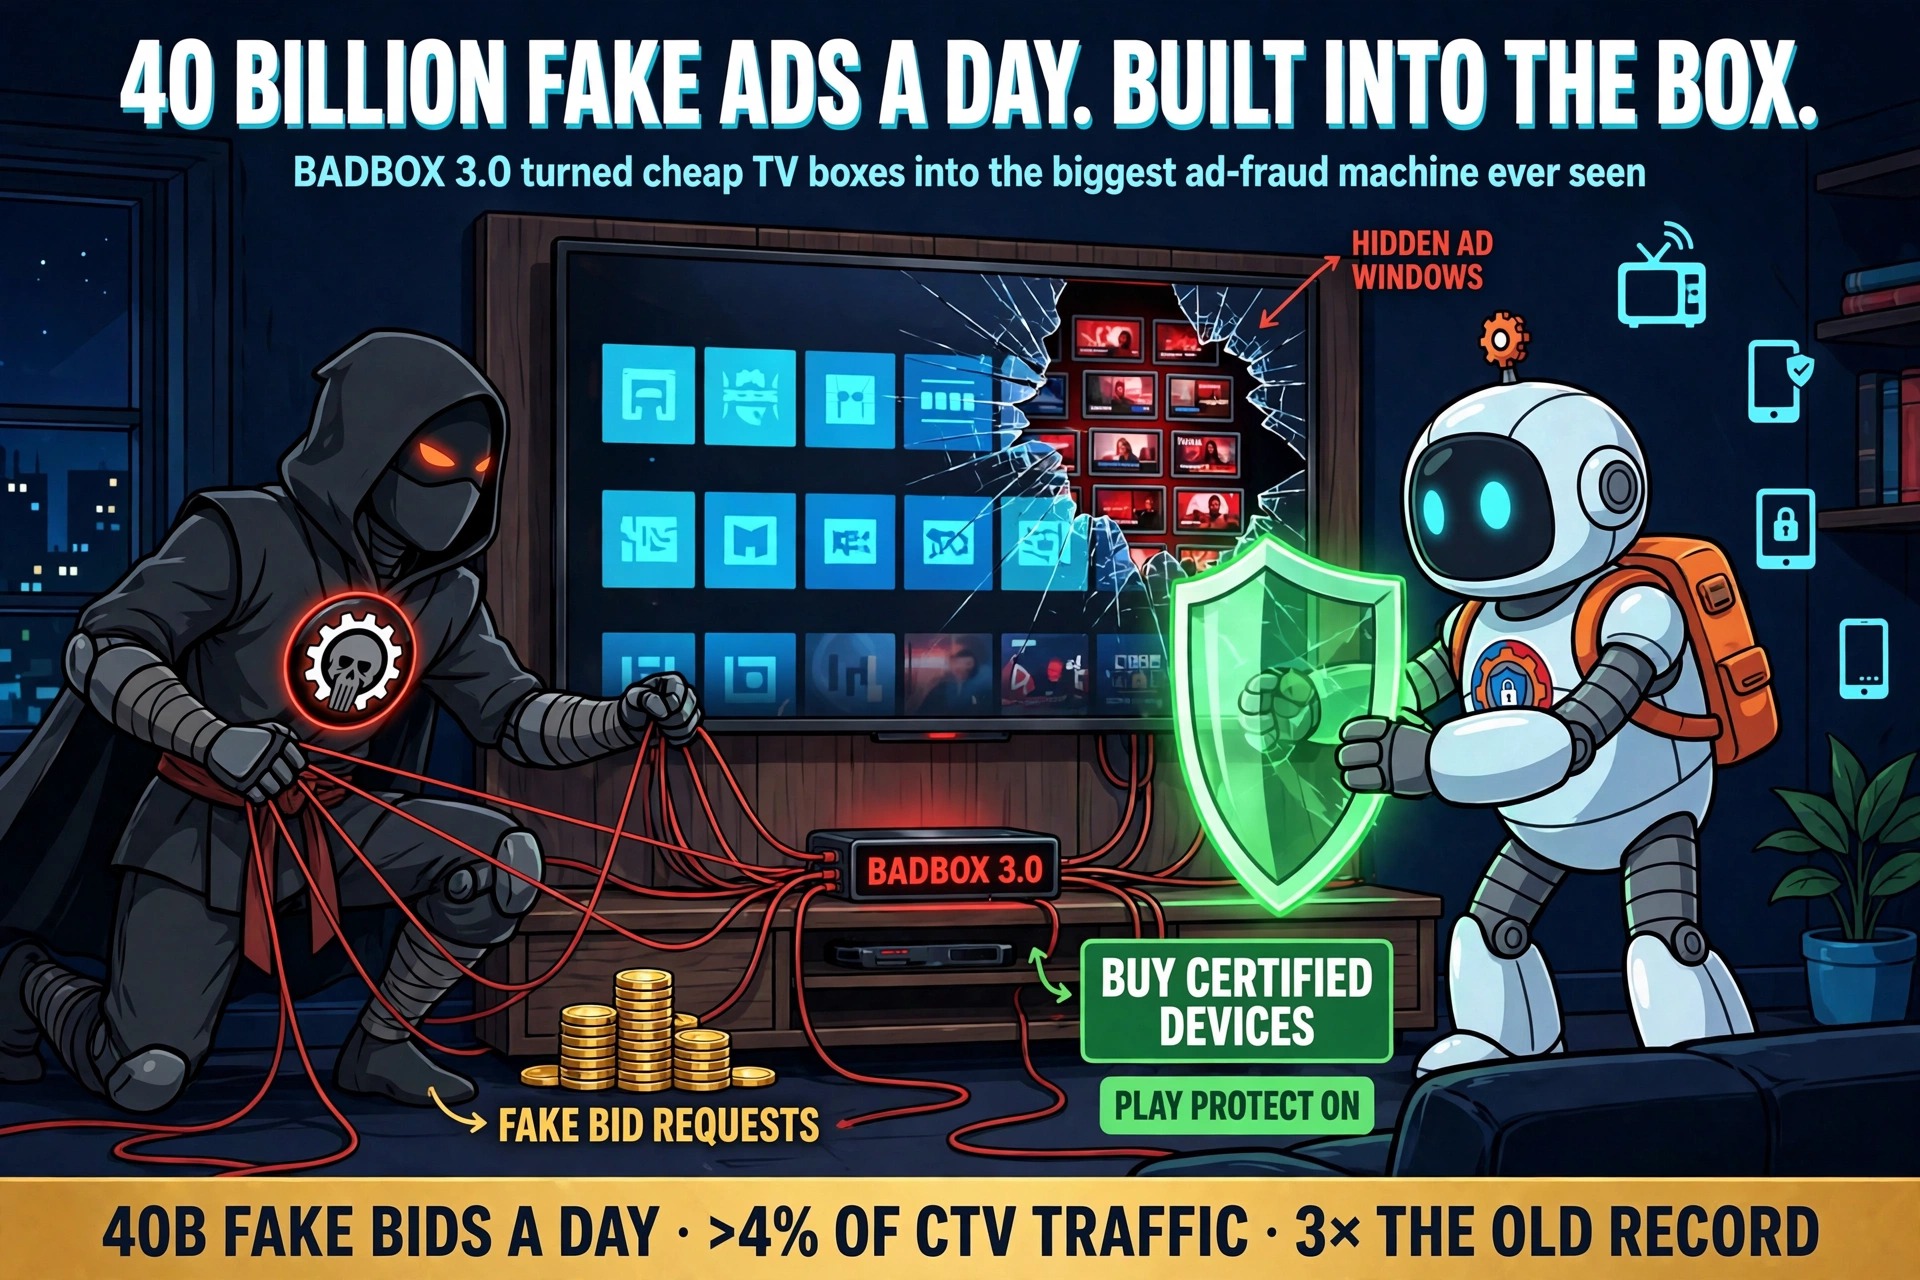
HUMAN’s Satori researchers have a new record holder — and it is not close. BADBOX 3.0, the latest rebuild of the botnet that hides inside cheap Android TV boxes, peaked at roughly 40 billion fraudulent advertising bid requests a day, more than 4% of all connected-TV traffic the researchers observed. By daily bid volume, it is the largest ad-fraud operation ever disclosed — more than three times the previous record holder, VASTFLUX, and a bigger peak than the last five years of Satori investigations combined.
The box did the work. The owner never saw it.
BADBOX infects cheap phones, tablets, and streaming TV boxes running the Android Open Source Project — the uncertified, bargain-bin hardware sold under dozens of brand names. Once the malware is in, the device plays video ads in hidden windows while impersonating legitimate streaming apps, so the bid requests look like real viewers watching real shows. Some of the fraud never involved a device at all: HUMAN also observed fraudulent server-side ad insertion requests that told advertisers an ad had played on a streaming device when no device and no video ad were involved.
Then there is the cover. A proxying module enrolled infected devices in one of eleven residential proxy networks without the owners’ knowledge or consent, and some of the ad-fraud traffic was routed through those proxies to look legitimate and slip past anti-abuse filters. One of the networks, PXYEDGE, is the rebranded successor to IpMoYu, a residential proxy service previously linked to BADBOX 2.0. PXYEDGE advertised roughly 200,000 proxy nodes; HUMAN’s monitoring saw unique connections peak at around 340,000.
Built in at the factory
BADBOX was first discovered in early 2023, on a T95 Android TV box bought on Amazon. In December 2024, Germany’s cybersecurity agencies warned the botnet had infected tens of thousands of devices. The researchers linked the malware to a specific Chinese electronics manufacturer through its domains, device-specific checks in the code, a factory-installed TV launcher, and a repository maintainer — the infection was baked in before the box ever reached a living room.
The infected devices fetch their malware modules from public code repositories, and the same payloads are mirrored across hosting platforms for redundancy and to resist takedowns. It is the same public-code supply chain that has carried fake security tools and backdoors before — downloaded a scanner, installed a backdoor — except here the download is the device’s own update channel, and the victim bought the hardware.

Disrupted twice. Rebuilt twice.
This is not the first time BADBOX has been knocked down. In March 2025, HUMAN and Shadowserver cut more than 500,000 BADBOX 2.0 devices off from their control servers, and Google removed 24 apps that spread the malware from Google Play. Google later sued the botnet’s operators, saying BADBOX 2.0 had infected more than 10 million Android-based devices by April 2025.
It did not stop them. The operators rebuilt, and the rebuild set the record. HUMAN says it also participated in Google’s disruption of the related XCPE malware operation earlier this month — the backdoor was built in, 1.3 million TVs — which included taking down multiple command-and-control domains used by BADBOX 3.0. One of the malware repositories was taken down as well, and HUMAN says its systems now filter fraudulent advertising traffic associated with BADBOX 3.0.
But HUMAN’s warning is blunt: the operators are likely to adapt to the latest disruption, as they have done in the past. Every takedown so far has bought time, not an ending. The March 2025 disruption cut off half a million devices; eighteen months later the botnet was back, three times bigger than the last record holder.
What to do now
1. Buy certified Android devices from reputable manufacturers. The entire BADBOX model depends on cheap, uncertified hardware with malware baked in at the factory. A certified device from a known brand is not a guarantee, but it removes the factory backdoor from the equation.
2. Make sure Play Protect is available and active. It is the one on-device check that can flag the modules BADBOX pulls down after the box is plugged in.
3. Treat a bargain TV box as untrusted hardware. If a box arrived with apps you did not install, a launcher you cannot change, or ads playing when nothing is open, it is not a quirk. It is the product working as its maker intended — for someone else.

Forty billion fake bids a day is not a story about one bad app or one careless click. It is a story about hardware that arrives compromised, an ad market that pays for impressions nobody saw, and a botnet that has now survived two full disruption campaigns and come back bigger both times. The next version is already being built. The only question is whether the box it ships in is sitting on your shelf.